
We hack you,before attackers do.
One missed vulnerability can cost you a quarter of revenue. We’ve done 21,546 pentests. 5 in 10 had a High or Critical vulnerability.
A weak access rule can expose customer data.
We check exposed APIs, cloud storage, databases, and access controls first.
 2013
Every Yahoo account was compromised in the largest breach ever disclosed.
 2018
India's national ID database was reachable through insecure endpoints.
 2021
Scraped profile data for most users surfaced for sale online.
 2020
Account details for China's largest social platform were sold off.
 2018
Attackers sat in Starwood's reservation system for four years.
 2020
A misconfigured database exposed years of support logs.
 2024
A payments breach exposed medical and billing data nationwide.
 2017
One unpatched web server exposed the credit data of half the US.
 2013
A vendor login led to card data theft during the holidays.
 2019
A misconfigured cloud firewall exposed credit applications.
 2016
Uber paid hackers to hide a breach instead of disclosing it.
 2022
Health records leaked after a ransom demand was refused.
 2025
An exposed database leaked chat history and secret keys.
2013Every Yahoo account was compromised in the largest breach ever disclosed.
2018India's national ID database was reachable through insecure endpoints.
2021Scraped profile data for most users surfaced for sale online.
2020Account details for China's largest social platform were sold off.
2018Attackers sat in Starwood's reservation system for four years.
2020A misconfigured database exposed years of support logs.
2024A payments breach exposed medical and billing data nationwide.
2017One unpatched web server exposed the credit data of half the US.
2013A vendor login led to card data theft during the holidays.
2019A misconfigured cloud firewall exposed credit applications.
2016Uber paid hackers to hide a breach instead of disclosing it.
2022Health records leaked after a ransom demand was refused.
2025An exposed database leaked chat history and secret keys.
 2024
A data broker leak put Social Security numbers into open circulation.
 2019
A scraper pulled over a billion records from the Taobao platform.
 2024
A cloud breach exposed customer and ticketing data at scale.
 2021
Phone numbers and profile data leaked from an old scraping flaw.
 2016
An old credential dump became one of the largest ever leaked.
 2023
An API flaw let attackers match emails to accounts at scale.
 2013
Source code and customer records were stolen together.
 2014
Stolen employee logins opened the whole user database.
 2024
Call and text metadata for nearly every customer leaked.
 2014
A breach hit three quarters of US households' bank.
 2024
The library's authentication database was exposed and defaced.
 2023
Profile sharing turned credential stuffing into a genetic data leak.
 2022
Attackers stole backups of customer password vaults.
2024A data broker leak put Social Security numbers into open circulation.
2019A scraper pulled over a billion records from the Taobao platform.
2024A cloud breach exposed customer and ticketing data at scale.
2021Phone numbers and profile data leaked from an old scraping flaw.
2016An old credential dump became one of the largest ever leaked.
2023An API flaw let attackers match emails to accounts at scale.
2013Source code and customer records were stolen together.
2014Stolen employee logins opened the whole user database.
2024Call and text metadata for nearly every customer leaked.
2014A breach hit three quarters of US households' bank.
2024The library's authentication database was exposed and defaced.
2023Profile sharing turned credential stuffing into a genetic data leak.
2022Attackers stole backups of customer password vaults.
A 30-minute call is the whole setup.
You need no new software or security team. We scope, test, verify each finding, and send a report.
We agree on the boundaries, test accounts, and disclosure path before testing begins.
Our agents and researchers test the agreed product flows for security flaws.
A human checks each lead. We report it only when we can safely reproduce the exploit path.
You get proof, impact, and a fix for each finding. We retest after your team applies the fix.
We find the bugs attackers would use.
We give your engineers the proof and fix steps they need.
Password resets that leak tokens. Invites that outlive employees. Object IDs you can just increment. We test the routine flows teams rarely review twice.
Any authenticated user can download invoices belonging to other organizations by changing the numeric id. Reproduced on a test account. No customer data touched.
You get the request, the response, and the impact. We reproduce each issue by hand with test accounts.
Each finding includes a specific code or configuration fix. After your team applies it, we retest the issue.
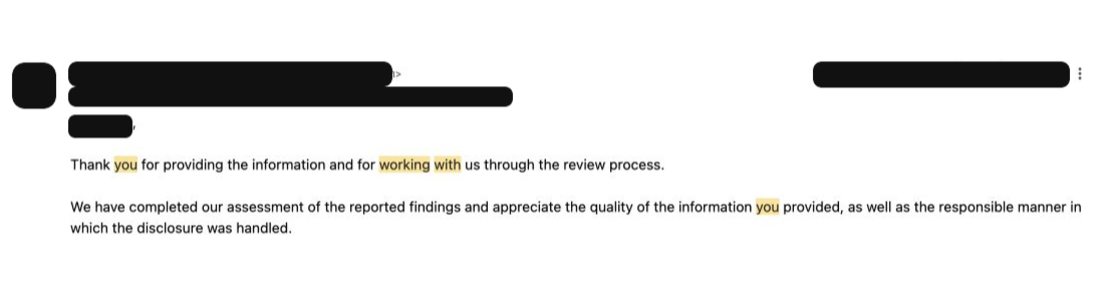
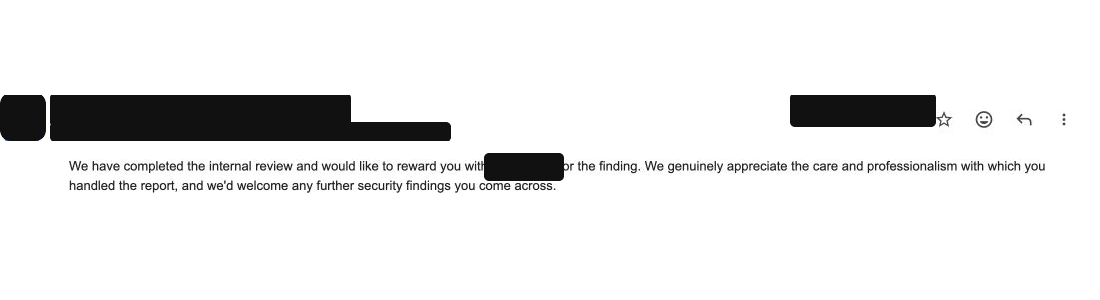
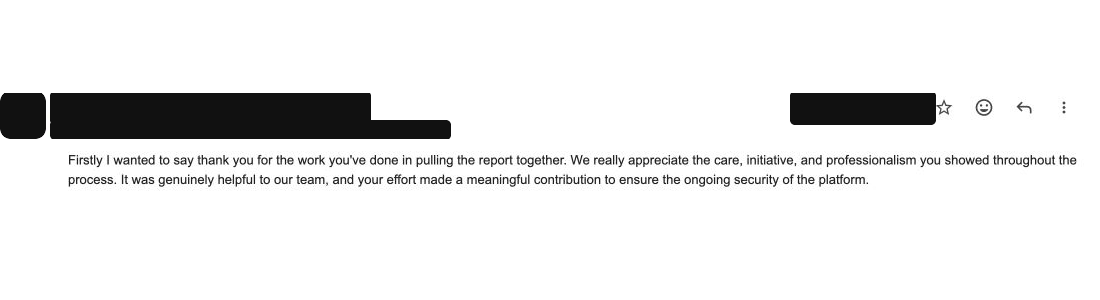
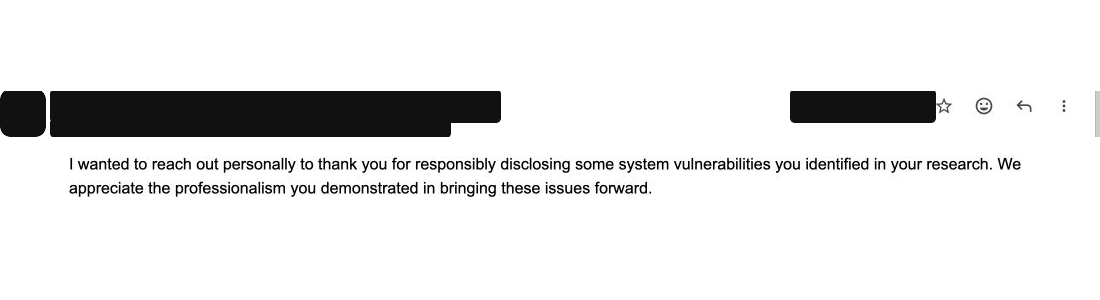
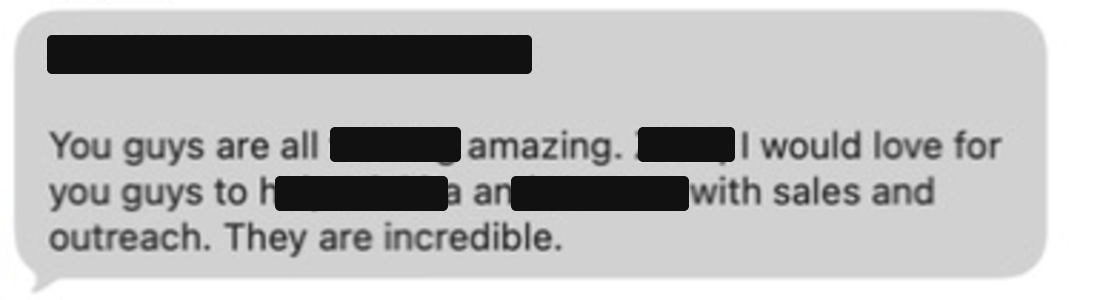
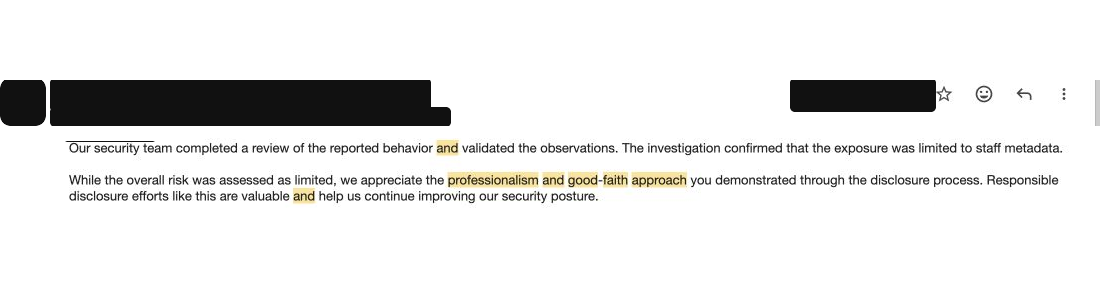
From the teams we reported to.
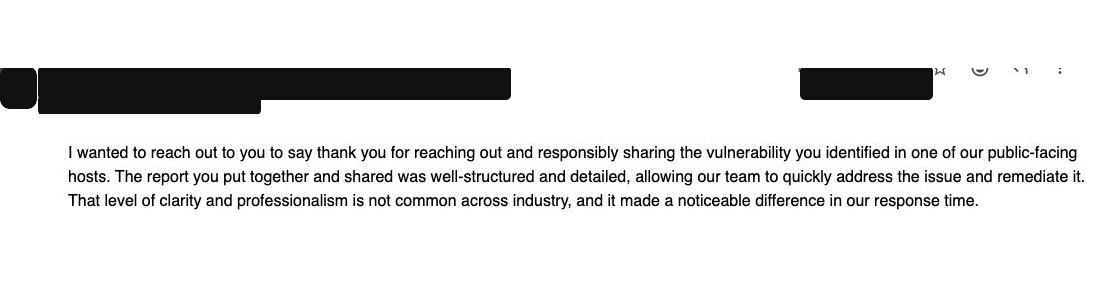
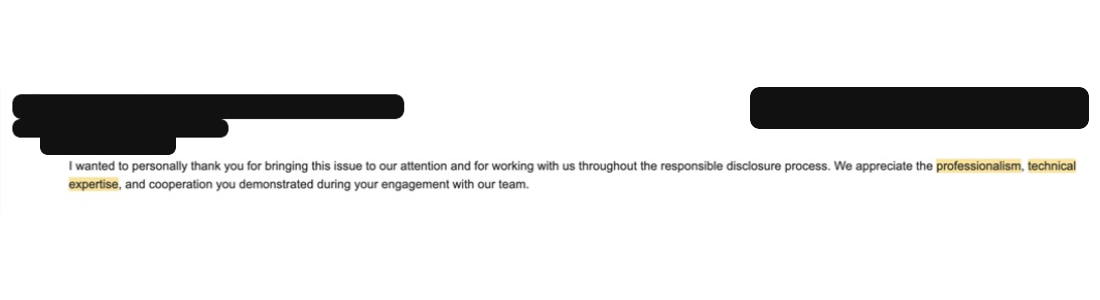
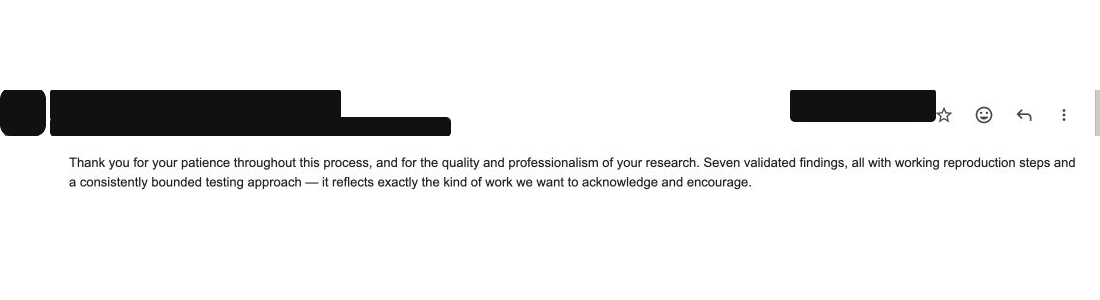
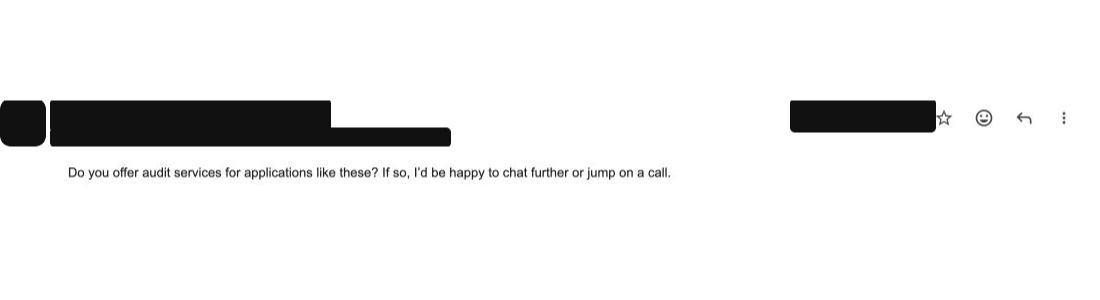
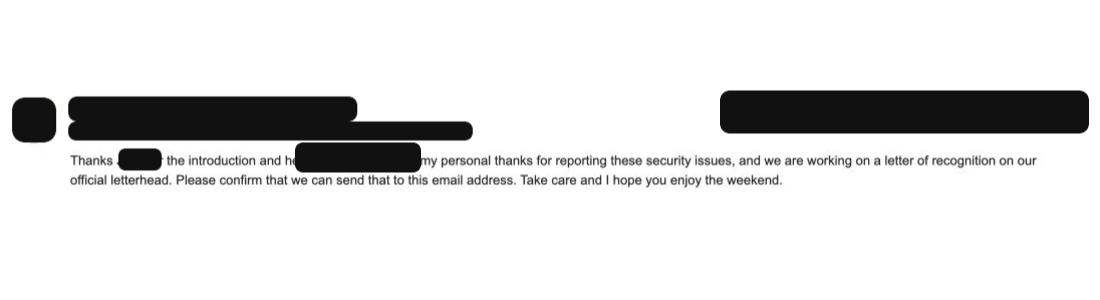
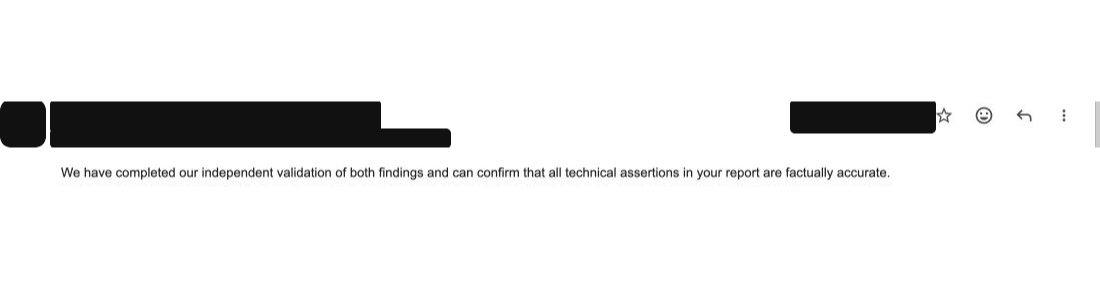
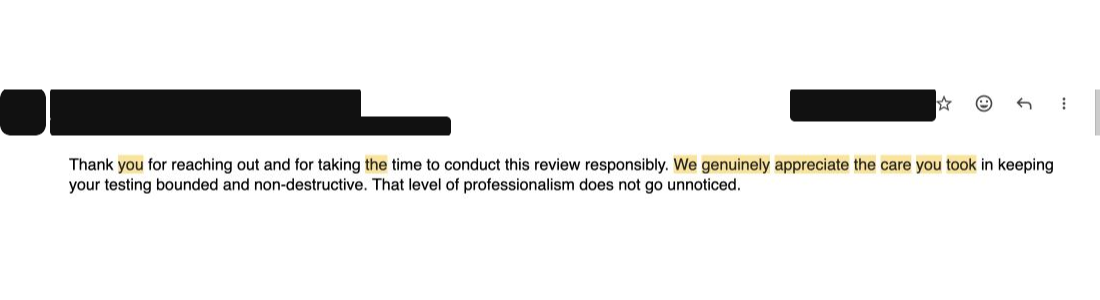
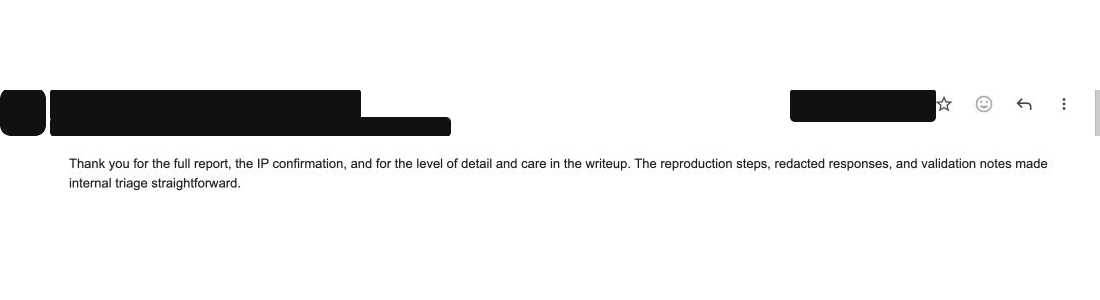
Vulnerability Management Manager
A report your engineers can use.
Each finding fits on one page: what broke, how to reproduce it, proof of impact, and a fix.
Testing stays within the agreed scope. Production customer data is off limits.
We confirm the impact of each critical finding. We discard weak scanner output before it reaches your team.
We contact the right team privately and share the details they need to fix the issue.
You do not need a security team or new software. We test the product and give your team clear fixes.
Questions teams ask first.
Is this just a scanner?+
Our proprietary automated systems find possible security flaws. A human researcher reproduces each reported issue and confirms its impact.
Will you touch our customer data?+
No. We use dedicated test accounts. Production customer data is off limits.
What do we get?+
A report with the affected system, steps to reproduce the issue, proof of impact, and a specific fix.
How fast can we start?+
Start with a 30-minute scoping call. You do not need to install software.
Find out what an attacker would.
Book a 30-minute call. We will walk through your product, how we test safely, and what we would go after first.